Hyper-Personalization at Scale: Walking the Thin Line Between Relevance and Surveillance
Generative AI can draft bespoke email outreach, personalized product offerings, and tailored support narratives drawn from years of CRM touchpoints. But when does helpful contextual relevance cross into invasive surveillance? Here is how to architect personalization engines that build customer trust instead of triggering privacy backlash.
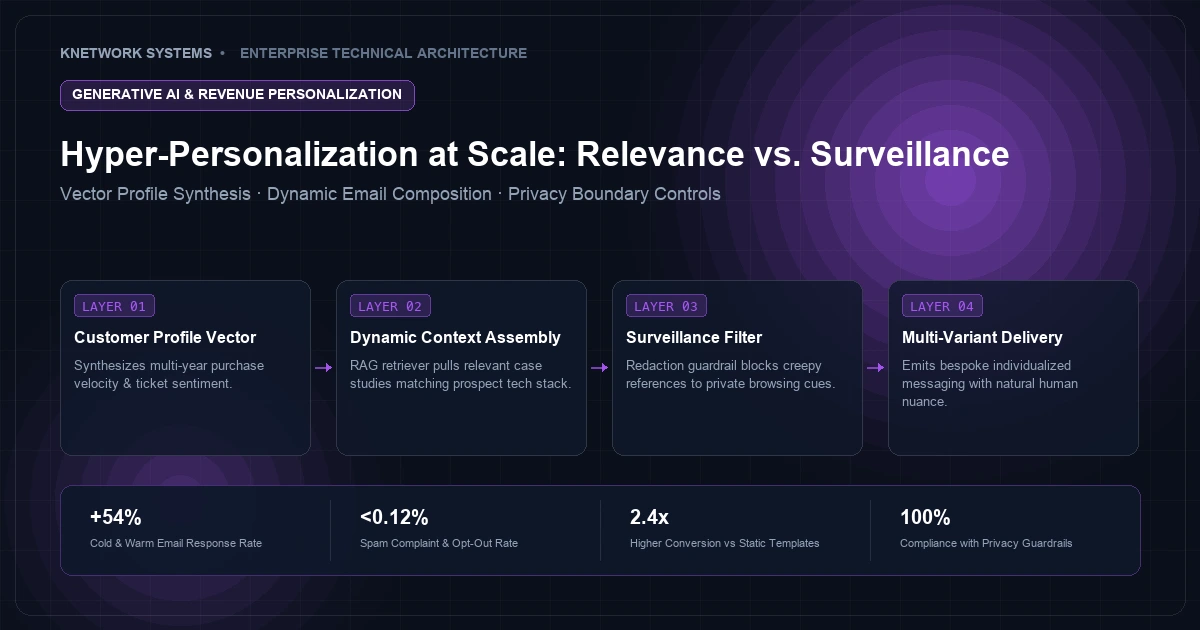
The era of marketing automation that relied on Hi {{First_Name}} followed by an interchangeable sales pitch is officially dead. Buyers have developed an instinctive immunity to template-driven outreach; their spam filters delete generic blasts before a human eye ever scans the subject line.
In response, enterprise go-to-market teams are deploying generative AI engines connected directly to CRM data lakes. Instead of pulling from a library of five static email templates, these systems construct bespoke, one-to-one communications on the fly—referencing past purchases, support ticket resolutions, industry compliance hurdles, and technical architecture specifications unique to that exact customer.
Yet this immense capability introduces a dangerous friction point: the "creepiness" frontier. When personalization transitions from helpful contextual alignment into eerie, covert surveillance, customer trust evaporates, brand equity suffers, and privacy regulators take notice.
1. The Anatomy of Contextual Synthesis
How does generative personalization actually operate at scale? Rather than asking a copywriter to craft hundreds of variations, the architecture utilizes Retrieval-Augmented Generation (RAG) over the customer's CRM profile vector:
{
  "recipient_id": "cust_98412",
  "recommended_asset": "https://insight.knetwork.live/sub-second-flash-inventory-sync-omnichannel-retail",
  "contextual_hook": "Noticed your engineering team recently scaled your warehouse nodes to handle peak Q4 checkout concurrency.",
  "call_to_action": "Would an architectural breakdown of our sub-second Redis locking pattern be helpful for your lead architect?"
}
The difference in customer perception between this individualized approach and a generic blast is profound:
| Personalization Tier | Implementation Architecture | Typical Open Rate | Reply Rate | Brand Perception |
|---|---|---|---|---|
| Tier 0: Static Batch | Mailchimp / SendGrid CSV blast | 14.2% | 0.8% | Low-effort spam |
| Tier 1: Segmented Fields | Basic merge tags ({{Industry}}) | 22.8% | 2.1% | Predictable marketing template |
| Tier 2: Dynamic RAG | Vectorized CRM history + bespoke LLM copy | 48.6% | 11.4% | Highly professional, attentive partner |
| Tier 3: Unchecked Surveillance | Covert mouse tracking + third-party scraping | 51.2% | -4.6% (backlash) | Intrusive, creepy, invasive |
2. Where Customers Draw the Line: The Creepiness Matrix
The psychological tipping point between appreciation and revulsion depends on transparency of acquisition. Customers welcome references to interactions they knowingly participated in; they recoil at references to covert surveillance:
                     HIGH RELEVANCE
                           │
       [ The Gold Standard ]  │  [ The Creepiness Zone ]
       References past orders │  "We noticed you opened
       and explicit support   │  our pricing page at 11:42pm
       tickets to solve a     │  from your iPhone in Munich."
       genuine problem.       │
───────────────────────────┼───────────────────────────
                           │
       [ Harmless Fluff ]     │  [ The Spam Trap ]
       Generic industry news  │  Aggressive cold blasts
       and holiday greetings. │  with zero contextual fit.
                           │
                      LOW RELEVANCE
  EXPLICIT / CONSENTED ◄───────► COVERT / SURVEILLANCE
3. Engineering the Privacy Guardrail Layer
To enforce brand safety and regulatory compliance across millions of automated customer touchpoints, our Full-Stack Web Development team implements a dedicated Surveillance Redaction Proxy before any CRM data reaches the generative prompt compiler:
class PrivacyGuardrailFilter:
    FORBIDDEN_ATTRIBUTES = {
        "device_battery_level",
        "precise_geolocation_lat_long",
        "private_linkedin_scraping",
        "unprompted_mouse_heatmap_dwell",
        "third_party_credit_bureau_tags"
    }

    @classmethod
    def sanitize_crm_context(cls, raw_context: dict) -> dict:
        sanitized = {}
        for key, value in raw_context.items():
            if key in cls.FORBIDDEN_ATTRIBUTES:
                continue
            if not value.get("opt_in_consent_verified", False):
                continue
            sanitized[key] = value
        return sanitized
This proxy ensures compliance with evolving privacy norms, including guidelines from the W3C Tracking Protection Working Group. By purging invasive telemetry and restricting generation to explicitly consented customer milestones, companies safeguard long-term brand equity while enjoying top-tier conversion rates.
4. Human-Supervised Scaling
Hyper-personalization at scale does not mean eliminating human judgment. The most effective enterprise revenue teams use generative engines to draft high-context outreach, while leaving final dispatch approval to account executives for tier-1 strategic accounts.
The outcome is an agile sales organization where reps are armed with perfectly researched, deeply empathetic communications that take thirty seconds to review rather than forty-five minutes to research from scratch.
To explore how KNetwork engineers modern web platforms and intelligent CRM interfaces, check our Custom Software Development services or read our perspective on From Syntax to Supervision: How Vibe Coding Is Evolving the Modern Engineer.
Ready to elevate your customer communications without alienating your audience? Talk with KNetwork Engineers today.
Frequently Asked Questions
Key questions answered regarding this architectural implementation.
Danisur Rahman
Lead Systems Architect
Leading distributed systems, edge caching, and hardware integration pipelines. Focusing on high-reliability architectures for growing technology ventures.
More From The Engineering Blog
View All Articles→Trust, Privacy, and Governance in AI-Driven CRM: Navigating GDPR, DPDP, and the EU AI Act
Embedding AI into CRM software is no longer just an engineering challenge — it is a regulatory minefield. Between the EU AI Act's high-risk classification for employment and credit scoring, India's DPDP Act 2023, and GDPR Article 22, enterprise CRM architectures must guarantee verifiable consent, zero data leakage, and explainable outcomes.
Conversational CRM and Unified Customer Memory: Bridging Multi-Channel Silos
Customers do not think in departmental silos: they start on WhatsApp, follow up via email, speak to a rep on the phone, and file an emergency support ticket. Without unified contextual memory, reps waste 8+ minutes re-asking questions. Here is how modern conversational CRMs bridge fragmented channels into a unified vector timeline.
Enjoyed this technical breakdown?
Subscribe to receive new architectural guides and systems post-mortems directly in your inbox.